Grade 12 results are out. Where to check yours

Unit notes and practice questions

Grade 9 Information Technology unit 5: Information and computer security

Everything here is for unit 5 of the Grade 9 Information Technology textbook: what the chapter covers, the short notes, practice questions with their answers, and the lesson video where one exists.

Get it on Google Play
5
Cards
10
Practice questions on unit 5
192–216
The textbook pages for unit 5

What unit 5 covers

  1. 1.Definition of Security
  2. 2.Principles of Computer Security
  3. 3.Computer Security Threats
  4. 4.Potential Losses Due to Security Attacks
  5. 5.How to Secure yourself and your Computer Systems
  6. 6.Unit Review Exercise

Short notes for unit 5

The cards filed under this chapter on the Grade 9 Information Technology page. Open one at a time.

PrincipleMeaningViolation Example
ConfidentialityRestricting data access to intended audience onlyUnauthorized person reading exam results
IntegrityEnsuring data is trusted, authentic, and not wrongly changedUnauthorized alteration of student marks
AvailabilityEnsuring systems and data are accessible when neededDoS attack halting banking services

When you use it

Use this to classify computer security requirements and evaluate whether a system protects privacy, correctness, or accessibility.

Watch out

Do not confuse confidentiality with integrity. Confidentiality stops unauthorized viewing, while integrity stops unauthorized modification.

Drafted from Grade 9 Information Technology, pages 192-216, then checked twice before it went up
Attack TypeMechanism
Denial of service (DoS)Floods targets with requests to block legitimate users
PhishingSends fraudulent emails appearing from reputable sources to steal data
Man in the middleIntercepts and steals data from communication between two parties
EavesdroppingSniffs unencrypted data transmitted across open networks
SQL injectionInjects unauthorized input into a database SQL query via a website
Social engineeringCreates a manipulative social situation to trick users into giving data

When you use it

Use this to identify the specific cyber-attack method described in a scenario or exam question.

Watch out

Phishing relies on deceptive messaging like fake emails, while Eavesdropping intercepts raw transmission traffic on open networks.

Drafted from Grade 9 Information Technology, pages 192-216, then checked twice before it went up
Loss CategoryDefinition
Destruction or loss of informationHardware breakdown or permanent loss of data
Corruption of informationUnauthorized alteration of stored files or records
Theft of servicesUnauthorized use of computer or network resources
Illegal usageUsing normal system functions for unlawful or harmful behavior
Disclosure of informationDisseminating private data to unauthorized individuals
Denial of useDegrading or blocking access to authorized users
Elevation of privilegeExploiting system weakness to gain higher user access rights

When you use it

Use this to categorize the specific damage or impact caused by an information security breach.

Watch out

Elevation of privilege is gaining higher user rights than assigned, while theft of services is using legitimate privileges for unauthorized purposes.

Drafted from Grade 9 Information Technology, pages 192-216, then checked twice before it went up

When you use it

Use this when explaining the balance between human behavior and technical safeguards in computer security.

Watch out

Remember that 90% of security relies on users following good computing practices, and only 10% on technical tools, not the reverse.

Drafted from Grade 9 Information Technology, pages 192-216, then checked twice before it went up

Malware TypeCore Characteristic
VirusReplicates itself to alter program functioning
WormIndependent program that infects via network devices
Trojan horseDisguises as a legitimate program to steal or damage
SpywareSecretly tracks user activities and information
RansomwareLocks system files and demands payment for release
Key loggerRecords keyboard strokes to steal credentials
AdwareAdvertising software that can slow down devices or install threats
BotnetsNetwork of infected machines remotely controlled by an attacker

When you use it

Use this to distinguish among different malicious software types based on their method of operation.

Watch out

A worm is an independent program that spreads over networks, whereas a virus requires host code or user actions to replicate.

Drafted from Grade 9 Information Technology, pages 192-216, then checked twice before it went up

Practice questions on unit 5

10 multiple-choice questions written against this chapter, each with its answer and the reason. Try one before you open the answer.

Question 1

Which Ethiopian federal institution was established to safeguard the country's national interest by protecting its information and information infrastructures?

  1. A.Ethio telecom
  2. B.Information Network Security Agency (INSA)
  3. C.Commercial Bank of Ethiopia
  4. D.Ministry of Innovation and Technology
Show the answer and why

Answer: B Information Network Security Agency (INSA)

Why

INSA (Information Network Security Agency) is the national security agency in Ethiopia with a mission dedicated to cyber security and protecting the country's information infrastructure.

Question 2

According to the 90/10 rule of computer security, what percentage of security defenses rely on the individual following good computing practices?

  1. A.10%
  2. B.50%
  3. C.90%
  4. D.100%
Show the answer and why

Answer: C 90%

Why

The 90/10 rule states that 10% of security countermeasures are technical, while 90% of security defenses rely on users adhering to good computer practices.

Question 3

What do the letters in the CIA security triad stand for?

  1. A.Control, Internet, and Access
  2. B.Confidentiality, Integrity, and Availability
  3. C.Cyber, Information, and Application
  4. D.Communication, Identification, and Authentication
Show the answer and why

Answer: B Confidentiality, Integrity, and Availability

Why

The CIA triad represents the three core principles of computer security: Confidentiality, Integrity, and Availability.

Question 4

Which type of malware locks files on a computer system and threatens to delete them if a payment is not made?

  1. A.Ransomware
  2. B.Adware
  3. C.Key logger
  4. D.Spyware
Show the answer and why

Answer: A Ransomware

Why

Ransomware is malicious software that locks files and data on a system and demands a ransom payment to release them.

Question 5

Ensuring that student marks in a school database are correct, authentic, and not wrongly changed relates directly to which security principle?

  1. A.Availability
  2. B.Integrity
  3. C.Confidentiality
  4. D.Denial of service
Show the answer and why

Answer: B Integrity

Why

Integrity means that data can be trusted, maintained in a correct state, and kept so that it is not wrongly modified by unauthorized parties.

Question 6

A student in Addis Ababa receives a fraudulent email pretending to be from Ethio telecom asking for their Telebirr password. What type of cyber attack is this?

  1. A.Phishing
  2. B.Eavesdropping
  3. C.SQL injection
  4. D.Denial of service
Show the answer and why

Answer: A Phishing

Why

Phishing is the practice of sending fraudulent communications that appear to come from a reputable source in order to steal sensitive data such as passwords or login information.

Question 7

Which type of malware is an independent program that spreads and infects computer systems through network devices?

  1. A.Worm
  2. B.Trojan horse
  3. C.Adware
  4. D.Rootkit
Show the answer and why

Answer: A Worm

Why

A worm is defined as an independent program that infects the computer system through network devices without needing a host program.

Question 8

What method of password attack occurs when someone physically looks over a user's shoulder to watch them type their credentials?

  1. A.Dictionary attack
  2. B.Brute force attack
  3. C.Shoulder surfing
  4. D.Rainbow table attack
Show the answer and why

Answer: C Shoulder surfing

Why

Shoulder surfing is a physical observation technique where an attacker watches over someone's shoulder to see their password or pin code.

Question 9

A student has access to the school internet connection for educational research, but uses it to advertise and sell clothing online. Which category of security attack impact does this represent?

  1. A.Corruption of information
  2. B.Theft of services
  3. C.Denial of use
  4. D.Elevation of privilege
Show the answer and why

Answer: B Theft of services

Why

Theft of services refers to the unauthorized use of computer or network services, such as using educational internet access privileges for online marketing.

Question 10

An attacker floods a bank's servers with traffic, causing CBE Birr and ATM services to stop functioning for legitimate users. What type of attack has taken place?

  1. A.Denial of Service (DoS)
  2. B.Spyware attack
  3. C.Social engineering
  4. D.Man in the middle
Show the answer and why

Answer: A Denial of Service (DoS)

Why

A Denial of Service (DoS) attack hurts computer systems by flooding the target with excessive requests, stopping regular users from connecting to timely network services.

The app holds 12 questions on this unit, marked as you go. These are the first 10.

The textbook pages for unit 5

Unit 5 runs from page 192 to page 216 of the Ministry of Education edition.

Ministry of Education edition, English, 251 pages

Download the PDF

Practise this unit in the app

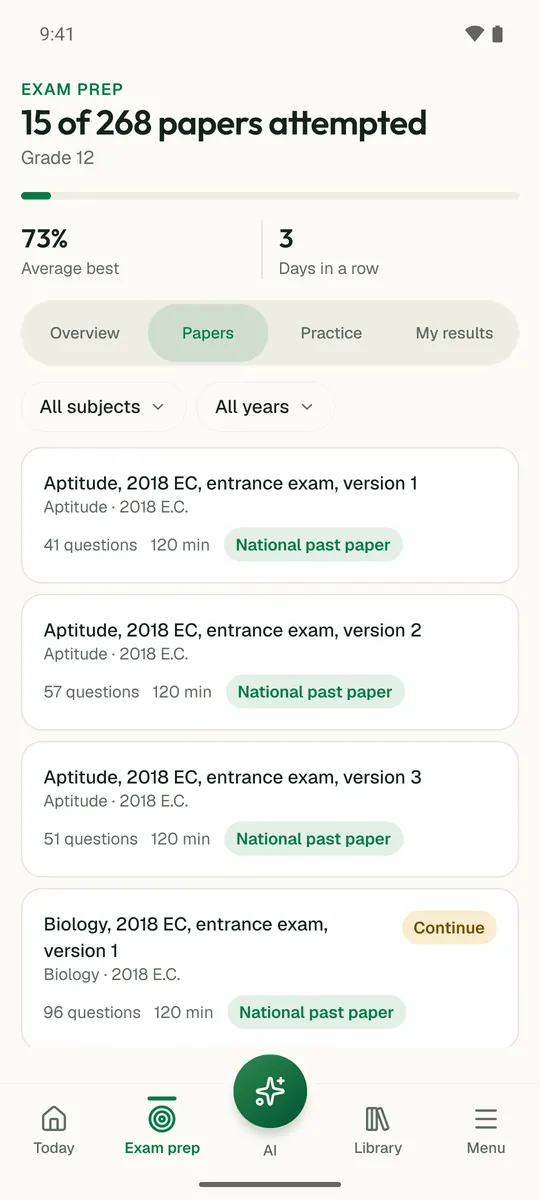
Temari turns this chapter into timed practice and marks it as you go, with an AI tutor to explain anything that did not land.

Start free

Temari.et is also an Android app, free on Google Play.

Sign inCreate your account